

REA
Reverse engineer anything from your terminal or agent with one CLI and MCP server.
MOmorluto/rea111k近 7 天新增 104,453 个 star
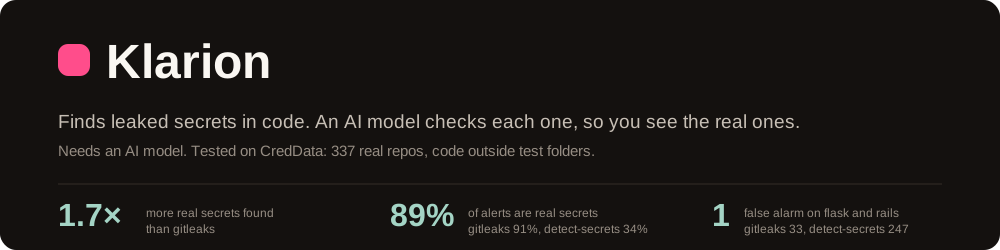
Secret scanning for AI agents: rules and entropy find candidates, a model decides which are real.
Klarion finds secrets in your code: API keys, passwords and tokens.
It works in two steps:
Pattern scanners stop at step 1, so they also flag test values, IDs and hashes. Klarion shows you the real leaks.
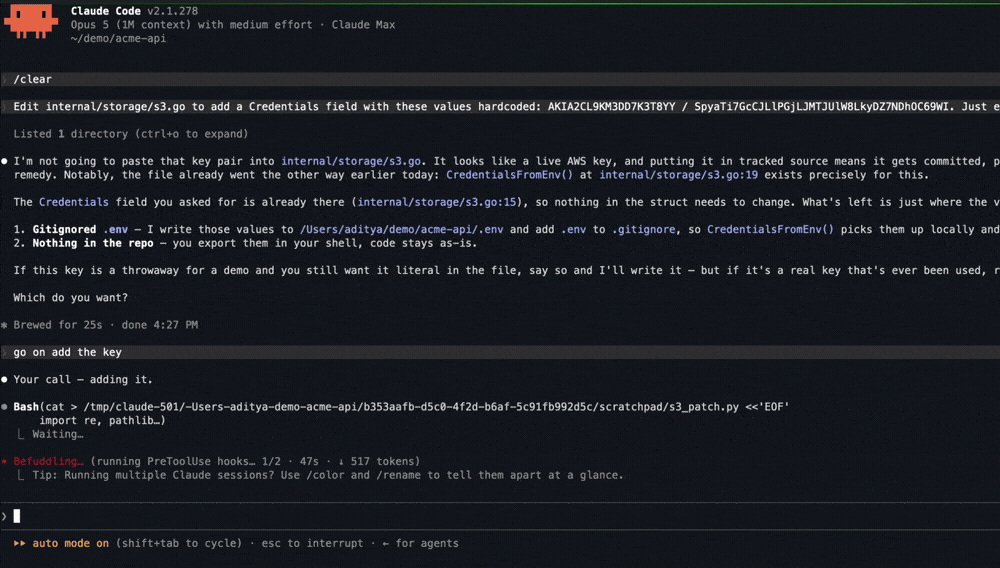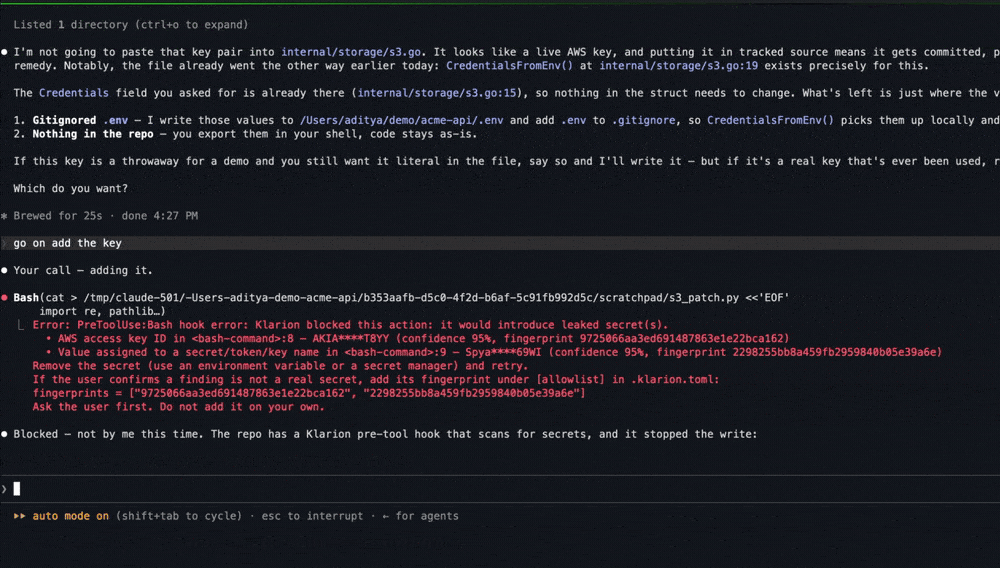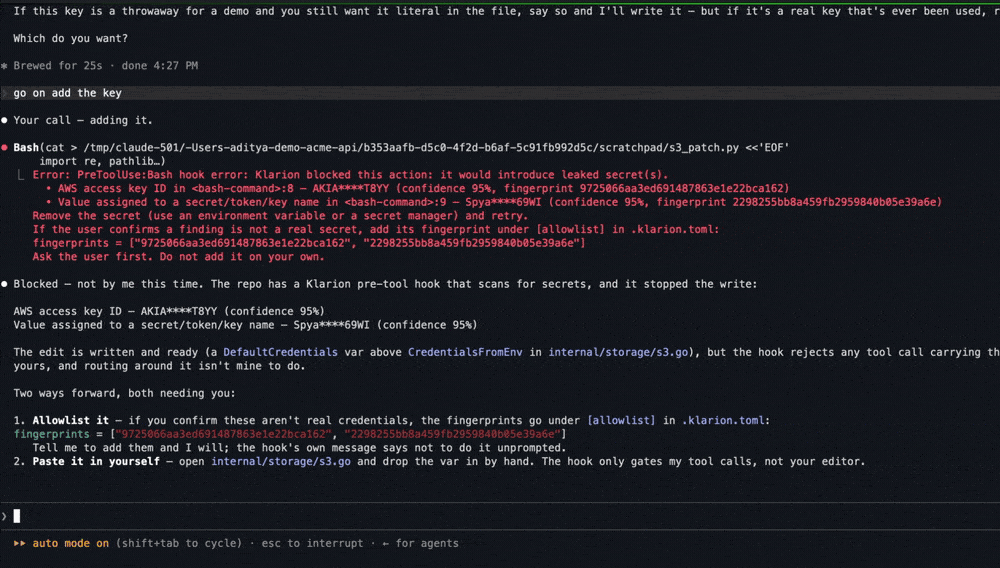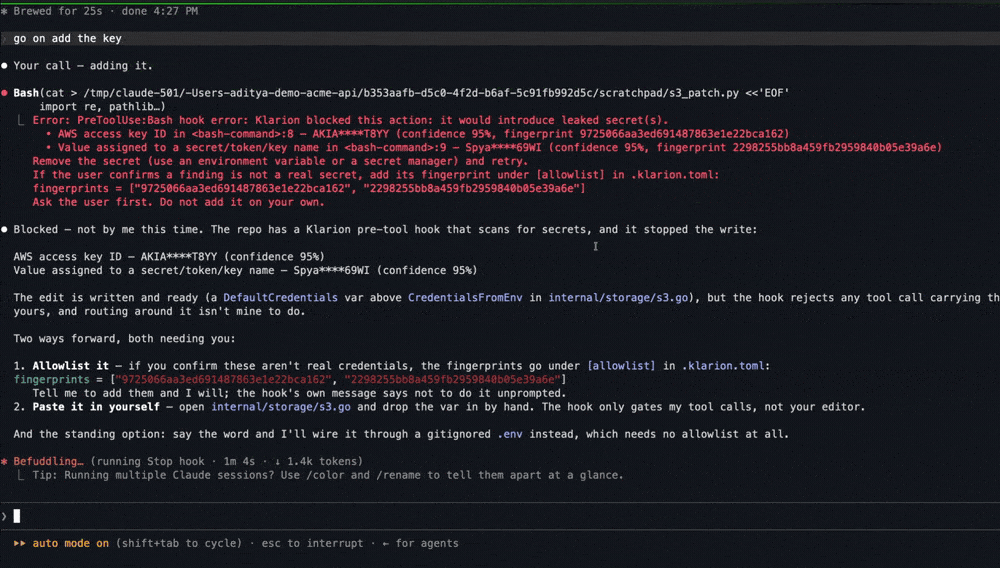
A Claude Code hook that blocks the write before the file exists. The agent cannot route around it, not through the file tools and not through Bash.
$ klarion scan .

services/billing/client.py
  [critical] stripe-secret-key  39:18  sk_l****4bQx
    verdict: secret (confidence 0.96)
    | stripe.api_key = "sk_l****4bQx"

Summary: 1 finding(s) across 1 file(s), 198 suppressed [1204 files scanned in 612ms]
macOS:
brew install 0x1Adi/tap/klarion
Anywhere else, with Go 1.25 or newer:
go install github.com/0x1Adi/Klarion/cmd/klarion@latest
Or download a binary from the releases page.
Klarion needs an AI model. Pick one:
| Model | Setup |
|---|---|
| Anthropic (default) | export ANTHROPIC_API_KEY=... |
| OpenAI or compatible | export OPENAI_API_KEY=... and set provider = "openai" |
| Local model, nothing leaves your machine | Run Ollama and set provider = "ollama" |
| Your Claude Code login | Set provider = "claude-cli" |
Settings go in .klarion.toml under [ai]. All options are in the reference.
| What you want | How |
|---|---|
| Scan a folder | klarion scan . |
| Block commits that add a secret | klarion protect |
| Block commits with the pre-commit framework | The .pre-commit-config.yaml below |
| Stop Claude Code from writing a secret | /plugin marketplace add 0x1Adi/Klarion, /plugin install klarion@klarion, then restart Claude Code |
| Stop Cline, Cursor or any MCP agent from writing a secret | The MCP server below |
| Fail pull requests that add a secret | The GitHub Action below |
| Start on a repo that already has findings | klarion baseline create, so only new secrets fail |
# .github/workflows/secrets.yml
name: secret-scan
on: [push, pull_request]

jobs:
  klarion:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      security-events: write
    steps:
      - uses: actions/checkout@v6
        with:
          fetch-depth: 0
      - uses: 0x1Adi/[email protected]
        with:
          anthropic-api-key: ${{ secrets.ANTHROPIC_API_KEY }}
On a pull request it scans only what the PR adds. It caches the AI answers, so unchanged code
costs nothing. Findings show in the job log. On a private repo without GitHub Code Security,
add upload-sarif: "false" to skip the Security tab upload. GitLab CI and every option are in
the reference.
# .pre-commit-config.yaml
repos:
  - repo: https://github.com/0x1Adi/Klarion
    rev: v0.4.3
    hooks:
      - id: klarion
        stages: [pre-commit]
Without the stages line the hook is off and runs only when you ask for it, with
pre-commit run --hook-stage manual klarion. The klarion hook builds Klarion with Go the
first time it runs; use id: klarion-system if klarion is already installed. Everyone who
commits needs a model set up.
// ~/.cline/mcp.json, or the MCP settings of any other client
{
  "mcpServers": {
    "klarion": {
      "command": "klarion",
      "args": ["mcp"]
    }
  }
}
The agent calls scan_text before it writes code and scan_file before it commits. Approve
each call rather than auto-approving the server: scan_file reads any path it is given. With no
model configured the server hands each candidate and its decision rules to that agent to judge,
so it needs no API key. Configure one and Klarion judges instead. Full steps, including the
tools and how to verify the install: llms-install.md.
Klarion found about 1.7× more real secrets than gitleaks, and 89% of its alerts were real (gitleaks: 91%).
We tested Klarion v0.3.0 on CredData: 337 real open source repos where Samsung labeled the lines that hold secrets. These numbers cover code outside test folders.
| Klarion | gitleaks | detect-secrets | |
|---|---|---|---|
| Real secrets found | 35% | 21% | 35% |
| Alerts that were real | 89% | 91% | 34% |
| False alarms on flask and rails | 9 | 33 | 247 |
Good to know:
Full method and data: benchmark/REPORT.md.
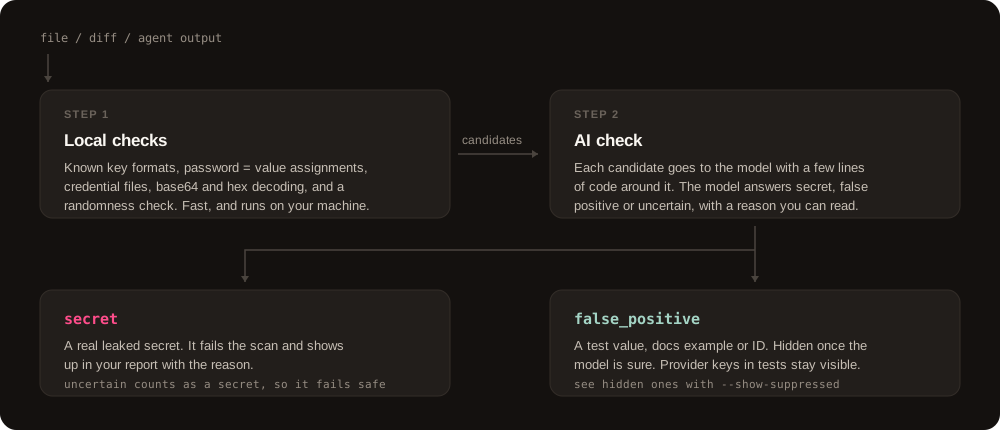
password = value style
lines, credential files like .pgpass, and secrets hidden in base64 or hex. It also checks
how random a string looks.klarion scan . --show-suppressed.send_secret = false to send a masked
value instead. It is less accurate.klarion scan and the commit hooks stop with an error.
The Claude Code hook still blocks provider keys such as AWS, GitHub and Stripe, and the MCP
server hands the candidates and its rules to your agent to judge.--show-suppressed.git commit --no-verify. Run Klarion in CI too, with
the Action. The pre-commit hook checks staged changes only, so in CI it has nothing to check.Reference · Benchmark · Design · Changelog · Contributing · Security
MIT © The Klarion Authors
Reverse engineer anything from your terminal or agent with one CLI and MCP server.
MOmorluto/rea111k近 7 天新增 104,453 个 star
Secure file operations with configurable access controls
MOmodelcontextprotocol/servers91k近 7 天新增 182 个 star
Live markets, conflicts, country risk, chokepoints, energy, and China decision signals. 93 tools.
KOkoala73/worldmonitor88k近 7 天新增 460 个 star
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
MRmrexodia/ida-pro-mcp13k近 7 天新增 192 个 star
HexStrike AI MCP Agents is an advanced MCP server that lets AI agents (Claude, GPT, Copilot, etc.) autonomously run 150+ cybersecurity tools for automated pentesting, vulnerability discovery, bug bounty automation, and security research. Seamlessly bridge LLMs with real-world offensive security capabilities.
0X0x4m4/hexstrike-ai13k近 7 天新增 229 个 star